 Chris Robert
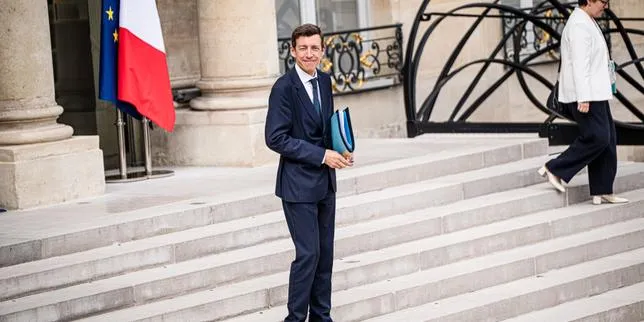
PARIS – A massive cyberattack recently crippled the digital infrastructure of the French Ministry of National Education in 2026, sparking serious concerns about data breaches involving millions of students and staff. This incident forced authorities to immediately launch a comprehensive security audit and accelerate the implementation of a double authentication system to ensure educational continuity and information protection.
Edouard Geffray, a high-ranking official at the Ministry of National Education, promptly reassured the public after the incident. We confirm that children will be able to return to their studies as soon as possible, he stated. This affirmation indicates maximum efforts are underway to restore disrupted services and minimize the psychological impact on the educational community.
The attack is strongly suspected to have originated from an organized hacking group, targeting central servers storing crucial data. Initial analysis suggests a security vulnerability was successfully exploited, allowing unauthorized access to administrative and academic databases.
The scale of this incident is significant. Millions of personal student records, ranging from full names, birth dates, addresses, to academic records and health information, are potentially exposed. Similarly, sensitive data of teachers and administrative staff are also at risk. The threat of such data breaches could lead to identity theft or other cybercrimes.
The French government, through the Ministry of Interior and the National Cybersecurity Agency (ANSSI), swiftly formed a crisis team. They are working closely with information technology service providers and external cybersecurity experts to trace the source of the attack, close vulnerabilities, and isolate infected systems.
A fundamental step taken is the execution of a thorough security audit. This audit focuses not only on the compromised system but also on the entire digital infrastructure of the Ministry of National Education. Its goal is to identify other potential vulnerabilities and strengthen cyber defenses holistically.
As a long-term response, the Ministry also announced the generalization of multi-factor authentication (MFA) for all user accounts within the education ecosystem. This system requires two or more verification methods to access an account, making it significantly more secure than a single password. Its implementation is expected to become the new standard for data security.
This incident highlights the vulnerability of the education sector, which often becomes an easy target for cyberattacks due to the large volume of data and sometimes less robust security infrastructure compared to the financial or defense sectors. In 2026, cyber threats have evolved to become more sophisticated and aggressive.
Cybersecurity expert Dr. Jean-Luc Dubois from Sorbonne University commented, This attack is a stark reminder that no institution is immune. Investment in cybersecurity must be prioritized, not just as a post-incident response, but as a continuous strategy.
The government's commitment to recovery and enhanced data security is strong. Edouard Geffray added, Our top priority is the protection of personal data and ensuring public trust in our digital education system. These measures demonstrate seriousness in facing the challenges of the digital era.
The implementation of multi-factor authentication will begin gradually, starting with staff accounts and then expanding to student accounts. Socialization and education on the importance of cybersecurity practices will also be promoted throughout school environments.
This event also triggered a national debate regarding budget allocation for cybersecurity in the public sector. Many parties are calling for significant increases in investment to counter evolving threats, to protect the nation's digital assets and its citizens.
Editorial Insight: The 2026 cyberattack on France's Ministry of National Education is not merely a technical incident; it reflects an increasingly complex digital threat landscape. The government's swift response, particularly its commitment to a comprehensive audit and multi-factor authentication, represents crucial steps. However, long-term success will depend on consistent implementation, continuous education, and adaptation to evolving hacker tactics. This incident underscores that cybersecurity is a vital foundation for the continuity of public services in the digital age.